
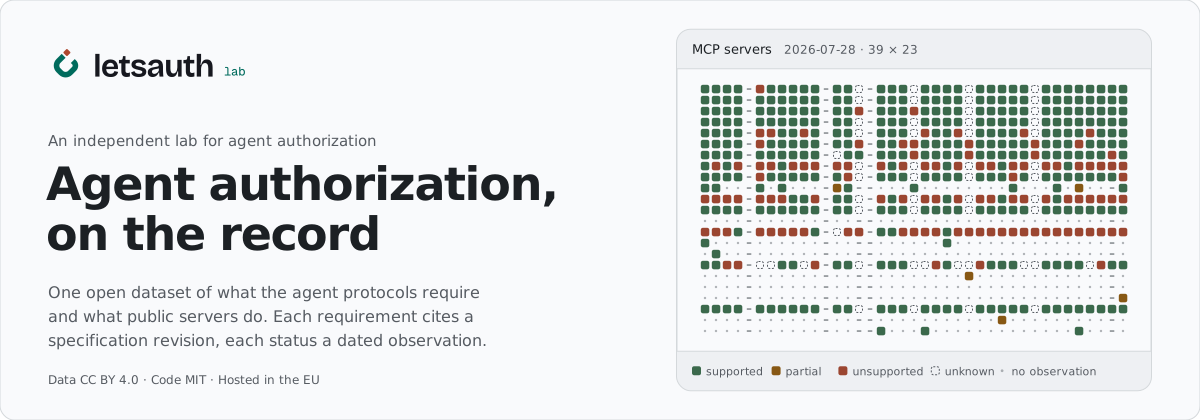
Let's Auth Labs is an independent, vendor-neutral lab for authentication and authorization in the agent era. MCP, A2A and agent delegation meet OAuth, OpenID Connect and workload identity, with a European lens. letsauth.eu is where its work is published.
Open the MCP auth atlas · See the standards map · Step through a delegation chain · Read a scanner report · Get the data
Vendors explain agent authorization through their own product. letsauth measures instead of asserting: one open dataset of what the agent protocols require and what real, public servers do.
- Every claim cites a revision. Each requirement links to the section of the specification revision it comes from.
- Every status cites an observation. A cell is a dated observation with a method and evidence a reviewer can open. An empty cell reads unknown, never failure.
- Open, append-only data. YAML under CC BY 4.0. Observations are never edited, so the atlas is also a record of how the ecosystem moved.
- Neutral and passive. Nothing is ranked, and the scanner reads public metadata only, never with a token.
- European by default. Hosting, storage and analytics run in the EU.
| letsauth | The site, the dataset, the schema and the passive scanner, in one repository. Code is MIT, data is CC BY 4.0. |
The most useful contribution is an observation: what a server you know does, with evidence a
reviewer can open. Start with CONTRIBUTING.md.
Security problems go to the private channels in SECURITY.md,
never to a public issue.